Active vulnerability analysis: how Zi0n protects your device
Modern consumer smartphones store our most confidential assets, yet their off-the-shelf operating systems remain plagued by zero-day security flaws weaponized by military-grade spyware such as Pegasus and Predator. Traditional antivirus solutions that merely cross-reference known file hashes cannot defend against zero-click infection chains requiring zero user interaction. Zi0n takes a radically different stance: continuous, proactive vulnerability analysis embedded into the core operating system, paired with physical and logical attack surface reduction.
Mobile exploits and the anatomy of a silent compromise
A software bug only turns into a catastrophic breach when an attacker finds a viable entry vector. On consumer hardware, adversaries frequently target underlying components that operate entirely outside user visibility:
- Baseband processor vulnerabilities: The cellular modem processes incoming radio signals before the primary OS even boots. A rogue cell tower (IMSI-catcher) can trigger memory corruption over the air without illuminating the screen.
- Multimedia parser flaws: Automated processing of image formats (WebP, JPEG) or video streams within popular messaging clients has repeatedly allowed attackers to achieve remote kernel execution.
- Abuse of accessibility services and UI overlays: Misleading applications request broad system permissions to silently log keystrokes, steal cryptocurrency private keys, and siphon ephemeral 2FA tokens.
- Physical USB intrusion: Public charging kiosks and specialized law enforcement forensic extractors (such as Cellebrite or GrayKey) leverage debug protocols like ADB to bypass standard lockscreen safeguards.
Active defense architecture and continuous monitoring in Zi0n
To stop sophisticated intrusion vectors before they reach your high-value assets, Zi0n deploys multi-layered active defense mechanisms across the entire device stack.
1. Dynamic kernel integrity checks and verified boot
Zi0n continuously validates the cryptographic signatures of system partitions, runtime kernel modules, and bootloader state. If an unauthorized entity attempts to modify volatile memory structures or escalate execution privileges, Zi0n terminates the suspicious process and isolates the partition immediately.
2. Strict sandboxing and isolated execution compartments
Every application deployed on Zi0n operates within an isolated sandbox governed by hardened SELinux security policies. Inter-process communications are strictly confined. Even if a third-party utility encounters an unpatched zero-day, the attacker remains trapped inside a locked compartment without lateral access to system keys or wallet credentials.
3. Network traffic inspection and C2 blocking via dVPN
A compromised payload must eventually establish an outbound connection to its command-and-control (C2) infrastructure to exfiltrate collected data. Zi0n routes all outgoing device traffic through a decentralized VPN (dVPN) featuring continuous IP rotation and encrypted DNS. Connection attempts to malicious nodes or suspicious command endpoints are severed instantly at the packet boundary.
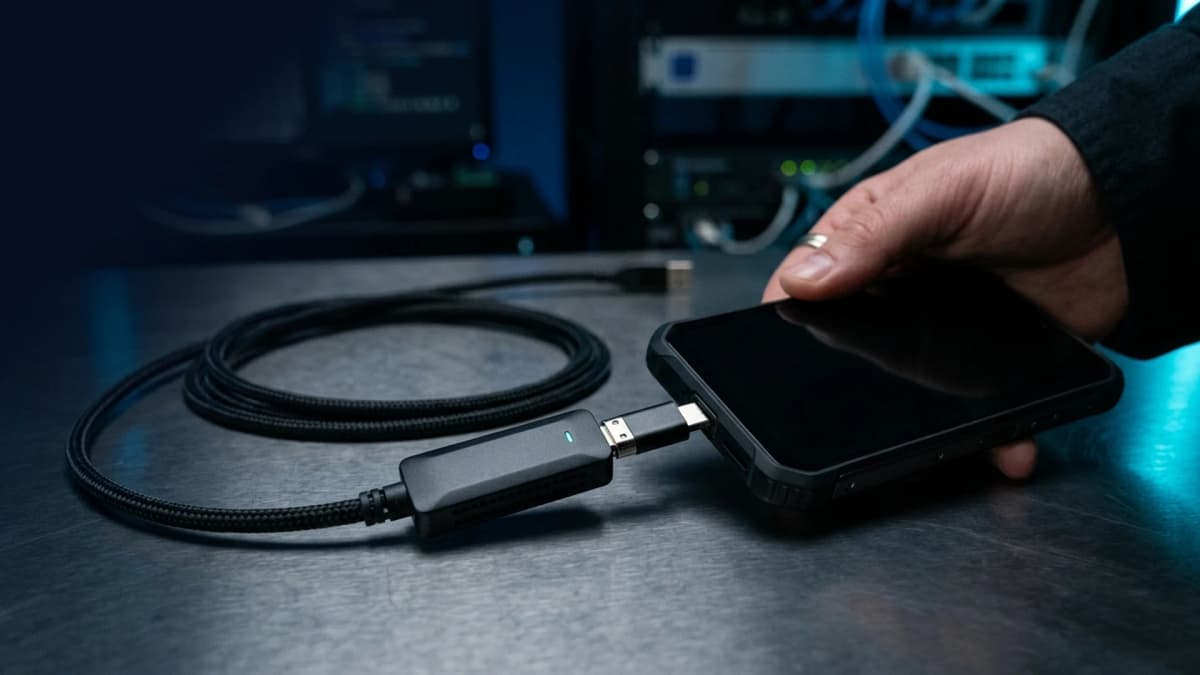
4. Physical USB interface protection with Cable Wipe
Physical connection attacks are among the most difficult to prevent on standard phones. Zi0n counters this threat with Cable Wipe technology: when an untrusted data cable or extraction box initiates an unauthorized data handshake, the device triggers an instant purge of volatile decryption keys from RAM, rendering all stored information cryptographically inaccessible.
5. Sensor disabling to neutralize surveillance vectors
Microphones and cameras are high-value surveillance targets for persistent malware. Zi0n provides hardware-level and logical controls to completely sever power and system access to cameras, audio inputs, and GNSS location modules whenever they are not explicitly active.
Practical steps to minimize your mobile attack surface
To safeguard your private keys and critical communications while traveling or operating in public environments:
- Disable automated wireless scanning: Keep Wi-Fi and Bluetooth disabled in transit to block unsolicited beacon requests and proximity exploits.
- Avoid untrusted charging ports: Use dedicated power-only charging adapters or rely on devices equipped with active Cable Wipe safeguards.
- Compartmentalize sensitive operations: Run financial transactions and confidential messaging on a dedicated, hardened terminal rather than on everyday consumer devices.
- Adopt security-focused operating systems: Mainstream monthly security patches consistently lag behind weaponized zero-day exploitation campaigns.
How can Zi0n help you?
For crypto investors, corporate executives, and high-profile individuals facing persistent surveillance risks, Zi0n transforms mobile communications into an impenetrable fortress. By uniting continuous vulnerability auditing, decentralized dVPN infrastructure, and anonymous global eSIM connectivity, your digital footprint remains protected against the most capable threat actors. Explore our complete hardware and software specifications at https://zi0n.io.
Frequently asked questions
How does Zi0n's active vulnerability analysis differ from an ordinary antivirus app? Traditional antivirus programs scan files against known malware databases. Zi0n operates at the architectural level, continuously verifying kernel integrity and halting abnormal process behavior in real time, neutralizing zero-day exploits before signatures even exist.
Does continuous system monitoring drain battery performance? No. Zi0n's active security controls are compiled directly into the hardened OS kernel and optimized at the hardware layer, ensuring negligible power overhead without heavy background scanning tasks.
Can Zi0n detect cellular interception by IMSI-catchers? Yes. Zi0n's cellular subsystem inspects radio network parameters to detect anomalous signaling, alerting users to forced 2G cipher downgrade attacks or fake base station connections.
What happens if an attacker connects a forensic extraction cable while the phone is locked? Zi0n's Cable Wipe feature instantly registers the unauthorized USB data handshake, purges encryption keys from volatile memory, and prevents forensic tools from extracting stored data.